Why Hybrid Web Filtering Is Becoming the New Standard for Schools
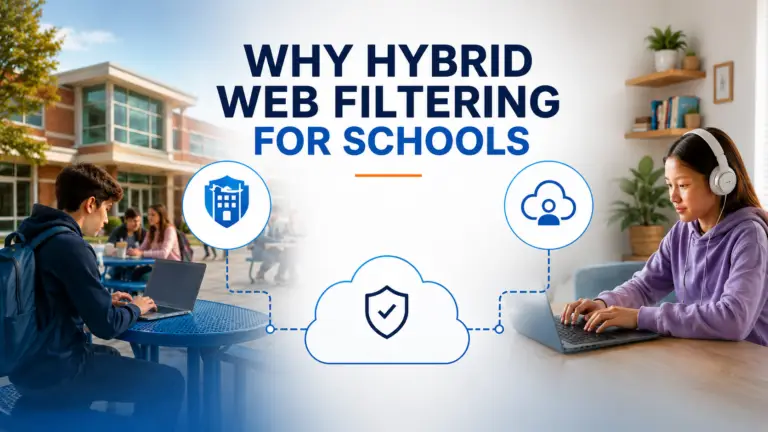
Cloud-first should not mean cloud-only. A hybrid approach provides the strongest filtering architecture applying the right enforcement method to each device, user, and network environment.
Web filtering has always evolved with the web. Early systems focused on blocking websites at the network perimeter. As the internet became encrypted, application-driven, and personalized, schools needed user-based policies, granular controls, application awareness, detailed reporting, and stronger protection against circumvention.
The next shift came with 1:1 programs and remote learning. By September 2021, 96% of U.S. public schools reported providing digital devices to students who needed them, and 97% of children ages 3 to 18 had home internet access in 2021.[1] [2] Filtering could no longer stop at the campus boundary. Cloud filtering clients became essential because they allowed policy, identity, and reporting to follow a managed device wherever a student learned.
Cloud-first was too often interpreted as cloud-only. Those are not the same strategy.
The School Technology Environment Is Broader Than the Managed Fleet
A district may standardize on Chromebooks, Windows laptops, iPads, or Macs, but those devices represent only part of the connected environment. School networks also support:
- Student and staff personal devices
- Guest systems and contractor devices
- eSports gaming consoles
- Smart panels, televisions, and digital signage
- Media players and devices with embedded browsers
- IoT equipment, lab systems, and specialized instructional technology
Many of these systems cannot run a filtering agent or browser extension. A cloud-only strategy can therefore protect the managed fleet, but leaves blind spots inside the school network itself.
Encryption Changed the Visibility Equation
Modern web traffic is overwhelmingly encrypted. Encryption protects privacy and data integrity, but it also means a filtering platform needs the right architecture and controls to identify risk within permitted web services, applications, searches, full URLs, and dynamically linked content.
This is particularly important in education, where allowing a major platform does not mean every page, video, comment, search, upload, or application behavior within that platform is appropriate for every student. Domain-level decisions alone cannot provide the same precision as URL, content, application, or session-aware controls.
Every Enforcement Model Has a Role
DNS filtering can provide a useful baseline for domain-level access control, but it lacks the deeper inspection, policy flexibility, and visibility available through enterprise-grade inline filtering. Similarly, many firewall vendors include web filtering capabilities, but these are typically designed as an extension of network security rather than as purpose-built K-12 web filtering platforms, which can limit the depth of customization, reporting, and education-specific controls.
A true hybrid web filtering architecture brings cloud filtering and transparent inline filtering together. Cloud filtering follows managed devices wherever students connect, while inline filtering protects traffic on the school network, including devices that cannot support a client. Working together, they provide broader coverage and more consistent enforcement without relying on a single filtering method.
- DNS filtering provides a useful domain-level security and access-control layer.
- Cloud clients protect managed devices across school, home, and public networks.
- Transparent inline filtering protects traffic from devices that cannot support a client.
Hybrid architecture is the operational model that coordinates those strengths rather than forcing every device and traffic flow through a single enforcement method.
Hybrid Is Not a Compromise
A hybrid filtering architecture uses cloud clients for managed devices and transparent inline enforcement for network-connected devices. The cloud follows the student. The appliance protects the campus.
That division of responsibility provides several advantages:
- Consistent off-campus protection. Managed devices retain user identity, policy, and reporting when students move between school, home, and other networks.
- Complete on-campus coverage. Unmanaged and specialized devices receive protection as soon as they connect to the school network.
- Local performance. On-campus traffic can be inspected locally rather than forcing every session through a distant enforcement point.
- Architectural resilience. Multiple coordinated enforcement methods maintain filter compliancy during outages or changes in network conditions.
- Operational choice. Districts can place enforcement where it best supports performance, visibility, privacy, and user experience.
Unified Control Matters as Much as Coverage
Hybrid should not mean fragmented. Schools should not need one product for remote laptops, another for guest devices, another for DNS, and separate reporting systems for managed and unmanaged devices. The goal is a unified policy framework and single pane of glass across all enforcement points.
A unified platform should allow administrators to manage and investigate:
- User, group, school, and IP-based device policies
- Exceptions, schedules, and granular web-service controls
- Application use and circumvention attempts
- Encrypted traffic inspection rules and exclusions
- Activity, alerts, reports, and incident investigations
- Both on-campus and off-campus activity from a central console
The Strategic Question Has Changed
The strategic question is no longer, “How do we move all filtering to the cloud?” The better question is, “Where should each policy be enforced to provide the best protection, performance, visibility, and experience?”
Cloud for managed devices. Inline filtering for complete network coverage. One platform for visibility and control.
What Education Leaders Should Ask
- Which device platforms can reliably support a filtering client, and which cannot?
- How are BYOD, guest, IoT, display, and eSports devices protected inside the school network?
- Can the platform distinguish domains from individual pages, searches, videos, applications, and dynamically linked content?
- How does the architecture inspect encrypted traffic while managing privacy, performance, and certificate requirements?
- Are policies, reporting, and investigations unified across cloud and inline enforcement?
- What happens if one enforcement path or connection is temporarily unavailable?
A Practical Path Forward
For most educational organizations, the future of filtering is not a binary decision between cloud and on-premises infrastructure. It is an architecture that recognizes how schools actually operate: students move, devices vary, traffic is encrypted, applications change quickly, and the campus network still carries systems that cannot be managed like a laptop.
Ativion ContentKeeper supports cloud, on-premises, and hybrid deployment models, with cross-platform clients and network-layer filtering designed to provide consistent policy enforcement and centralized visibility across managed devices, BYOD, guest access, and IoT environments.[5] The broader principle, however, applies regardless of vendor: effective filtering follows the user when necessary, protects the network when required, and gives the school one coherent system of control.
The future of educational web filtering is not cloud-only or network-only. It is hybrid by design.
Which Filtering Model Best Suits your District/School?
DNS, firewall, cloud client or inline filtering? Take the guesswork out of choosing the right approach.
This practical guide explains where each model works best, where coverage gaps can emerge, and how a hybrid approach can protect managed, unmanaged and specialist devices.
Use the evaluation framework and buyer checklist to identify the right architecture for your school or district.
Meet the Author
Daniel Castillo has been a lead ContentKeeper Network and Engineering Manager for close to eight years and prior to that was in the Waco, Texas school district where he managed network systems for a large school district.
Daniel C. is the Manager of Engineering at Ativion/ContentKeeper, bringing over 20 years of experience in K–12 education technology. Prior to joining Ativion, he spent 14 years as Network and Systems Coordinator at Waco ISD in Waco, TX. His technical expertise spans network infrastructure, cybersecurity, and systems management, backed by industry certifications from Cisco, Microsoft, VMware, EC-Council, and CompTIA. Grounded in firsthand experience, Daniel bridges the gap between vendor solutions and the lived realities of school districts. He also serves on the Waco ISD Education Foundation Board and remains committed to advancing digital safety, student well-being, and effective classroom technology in education.
Sources
[1] Technology Support. U.S. Department of Education, National Center for Education Statistics. Reports that 96% of public schools provided digital devices to students who needed them in September 2021.
[2] Children's Internet Access at Home. U.S. Department of Education, National Center for Education Statistics. Reports that 97% of 3- to 18-year-olds had home internet access in 2021.
[3] Cloudflare's 2025 Annual Founders' Letter. Cloudflare. States that well over 95% of internet traffic is encrypted.
[4] ContentKeeper. Ativion. Product information on deployment options, cross-platform coverage, network-layer filtering, and centralized management.